23 September, 2020

Triggered

Somebody pointed me to a research article about how many app developers fail to comply with the GDPR and data requests in general.

The sender suggested that I could use it in marketing for Nextcloud.

I appreciate such help, obviously, and often such articles are interesting. This one - I read it for a while but honestly, while I think it is good this is researched and attention is paid for it, I neither find the results very surprising NOR that horrible.

What, a privacy advocate NOT deeply upset at bad privacy practices?

Sir, yes, sir. You see, while the letter of the law is important, I think that intentions also are extremely important. Let me explain.

Not all GDPR violations are made equal

If you or your small business develops an app or runs a website to sell a product and you simply and honestly try to do a decent job while being a decent person, the GDPR is a big burden. Yes, the GDPR is good, giving people important rights. But if you run a mailing list on your local pottery sales website, with no intention other than to inform your prospective customers and followers of what you're up to, it can be a burden to have people send you GDPR takedown and 'delete me' requests instead of just having them, you know - unsubscribe via the link under your newsletter!

The goal of the GDPR, and of my personal privacy concerns, isn't at all related to such a business. If anything, their additional hardship (and we at Nextcloud have this issue too) is at best a by product of the goal. That byproduct isn't all bad - we all make mistakes, and being more aware of privacy is good, even for small businesses. The GDPR has forced many small businesses to re-think how they deal with private data, and that isn't a bad thing at all. But it isn't the main benefit or goal of the GDPR in my eyes. There are big businesses who totally COULD do better but never bothered, and now the GDPR forces them to get their act together. While that's a real good thing, even THAT is not, in my opinion, what the GDPR is about.

Privacy violation as a business

You see, there are businesses who don't violate privacy of people by accident. Or even because it is convenient. There are businesses who do it as their core business model. You know who I'm talking about - Facebook, Google. To a lesser but still serious degree - Microsoft and yes, even Apple, though you can argue they are perhaps in the "side hustle" rather than "it's their primary revenue stream" category.

For these organizations, gathering your private data is their life blood. They exploit it in many ways - some sell it, which is in my opinion definitely among the most egregious 'options'. Others, like Google and Facebook, hoard but also aggressively protect your data - they don't want to leak it too much, they want to monetize it themselves! Of course, in the process of that, they often leak it anyway - think Cambridge Analytica - that was in no way an incident, hundreds of apps get your private data via Google, Facebook, Microsoft and others. But by and large, they want to keep that data to themselves so they can use it to offer services - targeted ads. Which in turn, of course, get abused sometimes too.

My issue with this business model, even without the outright sale of data, is two-fold.

Ads work better than you think

First, in principle - while people might feel ads don't effect them, there is a reason companies pay for them. They DO effect your behavior. Maybe not as much or in the way marketing departments think or hope, but the effect exists.

How bad is that? Depends, I guess. To some degree, it is of course entirely legitimate that companies have a way to present their product to people. But modern targeting does more, including allowing companies to charge specific people different prices, and of course a wide arrange of sometimes nasty psychological tricks is used. The example Facebook once gave to potential advertisers, of targeting an insecure youth "at their most vulnerable" with an ad is... rather disgusting.

This gets worse when we're not just talking about product ads but political ads, either from political countries or, of course, from foreign non-democratic adversaries trying to influence our freedoms in a rather direct and dangerous way. And again - this is more effective than most people realize or are willing to admit and has swayed elections already, making is all less free.

Centralization is bad

Second, there is simply a HUGE issue with all-our-eggs in one basket. Especial when that basket is in a foreign country and not protected by privacy and security laws compatible with those in your own country. Having a single point of failure, how well protected - is just not smart. Things WILL fail, always. Better have slightly more breaches that each are just a single provider, than one breach of all private data of everyone in a country...

And that's not even talking about the fact that this data helps these companies get incredibly huge and then allows them to suppress or kill competition (or just buy it) - think Amazon, Microsoft. These tech molochs are just plain bad because of many reasons. They are anti-competitive, which raises prices, decreases choice, and the much lower innovation-per-dollar they produce is of course a worse deal for society too. They are too easy to control by law enforcement and censorship, impacting our freedoms - even when they're not 'foreign' to you. Yes, it is harder to censor 50000 private servers than one Google server farm!

Triggered

 So, as you notice, this question triggered me. Not all privacy violations are equal. Intentions matter. As does market power. And the GDPR is not a golden bullet. It has downsides - compliance is often easier for big companies than small ones, a serious issue.

Luckily, our judicial system tends to look at the intentions behind law, and I would expect a judge to fine an organization heavier for truly bad business models than for honest mistakes. I hope I'm not too optimistic here.

From my side, I don't want to bang on people's head for mistakes. I want to attack and challenge bad business models and bad intentions. A local, small app maker who fails to respond quickly enough to GDPR requests - not my target. Facebook - yes.

And by the way. Maybe it doesn't need to be said to most of you, dear readers, but of course - our open source world is, I still believe, a huge part of solving this problem. KDE, openSUSE and other Linuxes and desktops - and of course Nextcloud, Mastodon, Matrix and other decentralized and distributed and self-hosted platforms. We have ways to go, but we're making progress!


As I concluded to the person who triggered me - I know, this is far too long a reply to what they said


But it triggered me ;-)


Best reply over twitter, (twitter.com/jospoortvliet) or so, this awful Google platform makes commenting nearly impossible. And I know, the irony, replying on twitter, and I still have not moved away from blogger.com... Some day, some day. When I find time.

08 June, 2020

Collabora vs ONLYOFFICE

Since the Nextcloud Hub release switched from ONLYOFFICE to Collabora Online as default, lots of people have asked why. Is one better than the other? Let's talk about this.

History

Let me first say - the decision wasn't pure technical. As always, relations and other reasons play a role. I'll try to cover both aspects, but there is always more. With that out of the way, let's first look at how ONLYOFFICE got into Nextcloud.

Frank, myself and others in the Nextcloud community have wanted to integrate office in our collaboration platform for most of the past decade. Previously, we* had invested quite a bit in getting a collaborative document editor into our private cloud. The Documents app was a from-the-ground-up developed ODF editor with a unique and very clever design, built by KO GmbH (now sadly defunct). We together put resources in integration and further development and we hoped other (open source) businesses would invest and contribute too, so the solution would grow in time. Also, we had hoped some customers would be willing to pay for it. Both of these did not really come true, and KO sadly didn't survive.

* Note that I use 'we' here loosely as I wasn't really involved back then, so think 'the core team', as a slowly-changing team of people, including Frank, Jan, Arthur and others.

Fast forward to our launch on June 2 2016 (happy birthday!), and a few months later we announced Collabora Online integration. We had worked with Collabora to make this available not just to enterprise customers, as before, but to all users thanks to the 'CODE' docker image. As you know, we care deeply about community/private home users and this was of course a great step forward.

But running docker, setting up a reverse proxy on a second domain with proper certificates - it isn't easy and does not work for everyone. So we had to keep maintaining the Documents app a little, as some users still could only use that.

ONLYOFFICE vs Collabora

Meanwhile, a new open source online office solution came around, ONLYOFFICE. Let's talk for a sec how they compare Collabora, as the two could not be more technically and non-technically different!

Technical: how they work

The way Collabora Online works is:
An embedded version of Libreoffice runs on the server. It reads the document, then 'streams' the rendered document as image tiles to the browser client, which shows it to the user. The browser client does some of the menu's and lots of smart things like showing the cursor, other users, text selection etc, but many other components like pop-up menu's and sidebars are also streamed from the back-end, giving relatively good feature parity with LibreOffice. This strategy is responsible for giving LibreOffice, for example, desktop-level table style editing, better than any other online office solution.

The way ONLYOFFICE works is:
The document is converted on the server to a JSON file which is streamed to the browser client. The browser client is the full office suite, editing the document. Once done, it sends back the JSON and the server merges and exports it back to a file. A fully html5 canvas based front-end means a relatively pretty user interface and any javascript dev can go hacking.

So what does this mean?

  • LibreOffice is much heavier on the server and network connection, but uses a bit less client resources which tends to help mobile devices with battery life during editing
  • You get the full Libreoffice file type support. Decades worth of obscure file formats, it is all there.
  • ONLYOFFICE has a more modern UI, writing it all in Javascript so it is far easier to be mobile-friendly. You can imagine how useless those old LibreOffice paragraph settings dialogs are on a mobile phone screen!
  • In theory ONLYOFFICE would be much easier to integrate in web apps in general. Most app frameworks can consume a javascript or json component, a simply streamed, tiled image is far less flexible...

Compatibility

On document support, three things.

First, with regard to the Microsoft file compatibility - this is ALWAYS hit and miss. I can't objectively claim either is better or worse, you will always find a file that works well in one but not the other. But you will also find lots of MS Office files that won't work in Office 365, or break the desktop version between Mac and Windows or even just from older versions, because Microsoft screwed up their own compatibility.

Second, one thing I can say: if you migrate from Collabora Online to ONLYOFFICE and most of your files are ODF files because that's what Collabora uses by default, you're in for a bad experience. The ODF support in ONLYOFFICE is quite basic. But with MS Office files they feel on-par to me and that's what probably matters for most people. (sadly, yes)

Third, if you need any other file types - Collabora can handle a LOT, due to its long legacy. Word Perfect anyone?

For other technical capabilities - I probably be best off simply pointing to the comparisons both made themselves:

Social/historical differences

Let's talk about the second big difference between Collabora and ONLYOFFICE: their roots. Collabora builds on and is part of the LibreOffice community, a decades-old project, and consists of long time open source believers. Development is open and accessible and there are lots of individuals and companies that work on and can provide services for its code base. ONLYOFFICE on the other hand, is quite new to open source and only a bit over a dozen people have contributed to the code base. Their open core model if of course less than favorite in the open source world, though it is still miles better than proprietary - some people seem to lose sight of that sometimes, if you ask me. For an end user, the development model makes little difference, in either case.

let me emphasize two things.
First, it is awesome that we have TWO open source office suits. Building one is an amazing accomplishment - we have had others in the past but most are no longer really viable due to the massive amount of resources required to keep up.
Second, I think it is great that ONLYOFFICE decided to open source their product. I believe most people really under estimate what it takes to turn around your business model so radically. And if you're unhappy with decisions made, in either case - contribute, get involved. That is how you change things in open source.

Getting Office in Nextcloud

So, as I said in the History section, by 2017 we had three office solutions integrated in Nextcloud. One was easy to install but unmaintained and quickly deteriorating. The other two were harder to install but much more complete.

You know we're ambitious people, so indeed we have thought about and discussed this situation forever. And at some point, Robin started to really investigate what would be possible. After looking deeply at both, he finally managed to create a proof of concept with ONLYOFFICE. What he did was:

1. Separate the 'converter' part from ONLYOFFICE, the javascript front-end and the 'rest'
2. Made a separate binary of the converter, package the javascript and rewrite all the glue that lets them interact in PHP
3. Make this thing install-able as one big blob, acting as alternative 'server' with a proxy component that ties it all together

This was a LOT of work, but after polishing it, we had something we could show to the ONLYOFFICE people. They were initially not huge fans of what we did - no surprise, as it was an ugly solution. We discussed this for a fair bit and in the end, we agreed on an approach.

The result was what we made available last January with the first release of Nextcloud hub. We saw it as a first step towards deeper integration. Watch the video below to get an idea of what it looked like!

📺 view video on YouTube

And then...

After release, two things happened.
First, ONLYOFFICE has sadly been unable to focus much on the integration with Nextcloud. There was a long wish list we had - there is a lot you can do to make the experience nicer, from removing/disabling/hiding duplicated features like the build in chat and file handling to making file collaboration work in other apps like Talk, or adding certain features that connect even deeper like @mentioning users for example. Unfortunately, this didn't happen. No blame, there is a lot happening in the world right now!
Second, Collabora was inspired by the work and while we didn't think we could make it install-able with such ease, they obviously know their own technology better. And indeed, they did make it happen! Besides that, we worked with them to improve the already pretty good integration further, allowing you to edit documents while in a video call or chat in Talk.

As our focus continues to be on providing the best experience possible, we simply looked at that: what gives, right now, the best experience. And thus our latest video shows Collabora instead...

📺 view video on YouTube

Note that this doesn't mean we don't like ONLYOFFICE. 😍 This just changed the default you get on installation. Both solutions are very good and continue to be available for users! And perhaps things will change for the next release. Given the large differences at every level between the two, I consider it a benefit to have both approaches available for Nextcloud users!

So is Collabora better?

I will let Captain Marvel answer that.

03 April, 2020

Rant of the day: well, at least Microsoft is making loads of money...

Sadly, many if not most of our schools today are suddenly pumping lots of extra money into Microsoft, Zoom and other proprietary software companies, because they need online collaboration. We all know there are many alternatives to giving their students' data away to foreign companies but most don't bother. It is annoying, there is always budget for Microsoft, but not for proper, local, privacy-protecting open source solutions, even if those are better. Why is that?

Reputation, I'm convinced, is the main reason for that.

We teach them the wrong thing

Unfortunately, a lot of people try to convince schools, governments, charitable organizations and even companies to not pay anything at all. They are promoting open source solutions as an alternative that is cheaper or free, which just makes it look inferior to management. They are not telling organizations to pay local and open source product companies instead of Microsoft.

Open source/Free Software advocates hammer on "but it is free"! And when they do, THEY probably think of Freedom. But the person they talk to just thinks "cheap and bad", no matter how you try to explain freedom. Nobody gets that, really, even if they nod friendly while thinking what a silly, idealistic nerd you are. Been there, done that.

I love the enthusiasm, yes, but in the end it is not helpful: it presents open source as a crappy but cheaper alternative without any real support. Well, there are a few overloaded volunteer enthusiasts who might do a great job for a volunteer but can't compete with a bunch of full time paid people at Microsoft. So the schools and governments and companies will simply use those 'free' (as in cheap and crappy) services as a stop-gap and then beg their bosses for budget to be able to pay a "proper" Microsoft service. There goes more public money in NOT public code.

We need to stop teaching companies that open source is a crappy, cheaper alternative to proper, paid alternatives from big American companies and instead tell them that they can pay for an open source solution that has real good support, no vendor lock-in, doesn't leak your data, protects your privacy and is actually better in many other ways. That way open source companies can actually hire people to make products better instead of just doing consulting one customer at a time.

And yes, some companies and some business areas have figured this out - Red Hat and SUSE are obvious examples, and projects like OpenStack have lots of paid people involved. But lots of other companies, from Bareos (backup) to Kolab (groupware) have struggled for years if not decades to build a product, instead getting sucked into consulting.

It doesn't work that way

I have seen loads of open source product companies go bankrupt or just give up and become consulting firms because their customers simply expected everything for free and to only pay a bit for consulting. Lots of open source people work at or set up their own consulting firms, occasionally even contributing a patch to upstream - but not building a product. Not that they don't want to, but they quickly find out that working your ass off for a maybe decent hourly rate does not leave you time to actually work on the thing you wanted to improve in the first place.

Indeed, you can't build a good end user product that way. Frank and myself put together a talk about this recently:


I have also recently written an article about this entire thing, explaining why of all the business models around open source, only subscriptions can lead to a sustainable business that actually builds a great product. Will hopefully soon be on opensource.com.

Yeah but volunteers...

Are fundamental to open source, yes, no doubt. At Nextcloud we could not have build what we did without lots of volunteers, heck, nearly everybody at Nextcloud was a volunteer at some point. And yes, all code we write is AGPL, and that, too is important. I am NOT arguing against that, not in the least.

What I say is:
  • You can't build a great product without paid developers*
  • You can't build a great product on consulting and only getting paid for setting it up/hosting
But let me then also add:
  • You can build a better product collaboratively
  • And the (A)GPL are the best licenses to do that

I'm sure there are exceptions to those rules, yes. But compare a great product like Krita, see how its developers struggle every day to be able to pay the bills of just a few full-time volunteers. Do you know how they are currently paying most of them? Last time I spoke to Boudewijn, the reality was sad: the Microsoft App store. Yup. How many does Adobe manage to pay to work on its products? Why should our ambition not be to have as many people working on Krita? Of course it should be. And yes, keep it open source. Is that doable?

Of course it is. Well, maybe not Adobe levels, but we can absolutely do better.

Missed opportunities

I said this was a rant, so I do have to complain a bit. My biggest regret is that KDE failed to catch up during the netbook period (around 2005). I believe that it is in no small part because we failed to work with businesses. Idealism can be super helpful and can also totally keep you irrelevant.

KDE is, lately, working more with companies, trying to build up more business around its product. GNOME has been far better at that for a far longer time, by the way. It is hard, and companies like Kolab, struggling for the last ~20 years to make things work, have shown that. Just being a for-profit obviously doesn't solve all problems. Idealism and hard work are not enough to make a business work. But we can do better, and Nextcloud is an example that shows we can. Now not all things are freaking awesome at Nextcloud, really - we work our a**** off and it is hard. We put on our best face in public but sometimes I just want to bang my head on and in the wall...

Still, see the video, read the blog hopefully soon on opensource.com - there are ways.

Thoughts welcome.

Edit:
* let me qualify that statement. You can do it without paid developers in a small project, I dunno, grep or ls or the awesome simplescreenrecorder and tools like that. With those there is a risk of the apps going unmaintained and new ones popping up all the time - look at music players in the KDE community. I'd rather see one well maintained than new ones pop up with all their different flaws, but I totally get that for a volunteer it is often easier and more fun to start fresh. In either case, once you start building something huge, it gets pretty hard without long term dedicated resources. Note that it can be donations-run (like Krita and many others), with a charitable organization. I do think it is about more than 'just' the resources. If somebody 'just' sponsored 25 people to work full-time on Nextcloud, the end result would be different than the situation today. The need to deliver something that makes customers happy (which means focus on details, scalability etc!) and pressure to do things you wouldn't want to do in your free time (developer documentation...) make a big difference.

In any case, I really don't think projects like LibreOffice, Firefox, Nextcloud, KDE or GNOME and the Linux kernel itself would be where they are today without people paid to work on them.

07 September, 2019

04 September, 2019

Principles

dafuq?
We recently did a post about the Nextcloud Mission and Principles we discussed at the previous Contributor Week. I guess it is mostly the easy-to-agree on stuff, so let me ruin the conversation a bit with the harder stuff. Warning: black and white don't exist beyond this point.

Open Source

In an internal conversation about some community pushback on something we did, I linked to islinuxaboutchoice.com - people often think that 'just' because a product is open source, it can't advertise to them, it has to be chock full of options, it has to be made by volunteers, it can't cost money and so on...

But if you want to build a successful product and change the world, you have to be different. You have to keep an eye on usability. You have to promote what you do - nobody sees the great work that isn't talked about. You have to try and build a business so you can pay people for their work and speed up development. Or at least make sure that people can build businesses around your project to push it forward.

I personally think this is a major difference between KDE and GNOME, with the former being far less friendly to 'business' and thus most entrepreneurial folks and the resources they bring go into GNOME. And I've had beers with people discussing SUSE's business and its relationship with openSUSE - just like Fedora folks must think about how they work with Red Hat, all the time. I think the openSUSE foundation is a good idea (I've pushed for it when I was community manager), but going forward I think the board should have a keen eye on how they can enable and support commercial efforts around openSUSE. In my humble opinion the KDE board has been far to little focused on that (I've ran for the board on this platform) and you also see the LibreOffice's Document Foundation having trouble in this area. To help the projects be successful, the boards on these organizations need to have people on them who understand business and its needs, just like they need to have community members who understand the needs of open source contributors.

But companies bring lots of complications to open source. When they compete (as in the LibreOffice ecosystem), when they advertise, when they push for changes in release cycles... Remember Mark Shuttleworth arguing KDE should adopt a 6-month release cycle? In hindsight, I think we should have!

Principles

So, going back to the list of Nextcloud's Mission and Principles, I say they are the easy stuff, because they are. They show we want to do the right thing, they show what our core motivation was behind starting this company: building a project that helps people regain control over their privacy. But, in day to day, I see myself focus almost exclusively on the needs of business. And you know what, businesses don't need privacy... That isn't why we do this.

Oh, I'm very proud we put in significant effort in home users when we can - our Simple Signup program has cost us a lot of effort and won't ever make us a dime. The Nextcloud Box was, similarly, purely associated with our goals, not a commercial project. Though you can argue both had marketing benefits - in the end, a bigger Nextcloud ecosystem helps us find customers.

I guess that's what keeps me motivated - customers help us improve Nextcloud, more Nextcloud users help us find more customers and so both benefit.

Pragmatism and the real hard questions

Personally, I'd add an item about 'pragmatism' to the list, though you can say it is inferred from our rather large ambitions. We want to make a difference, a real difference. That means you have to keep focused on the goal, put in the work and be pragmatic.

An example is the conversation about github. Would we prefer a more decentralized solution? Absolutely. Are we going to compromise our goals by moving away from the largest open source collaboration network to a platform which will result in less contributions? No.... As long as github isn't making our work actively harder, does not act unethically and its network provides the biggest benefits to our community by helping us reach our goals, we will stay...

More questions and the rabbit hole

Would you buy a list of email addresses to send them information about Nextcloud? No, because it harms those users' privacy and probably isn't even really legal. Would you work with a large network to reach its members, even if you don't like that network and its practices? Yes - that is why we're on Facebook and Twitter, even though we're not fans of either.

Let's make it even harder. How about the choice of who you sell to. Should we not sell to Company X even if that deal would allow us to hire 10 great developers on making Nextcloud better for the whole world and further our goals? Would you work with a company that builds rockets and bombs to earn money for Nextcloud development? We've decided 'nope' a few times already, we don't want that money. But what about their suppliers? And suppliers of suppliers? A company that makes screws might occasionally sell to Boeing which also makes money from army fighters... Hard choices, right?

And do you work with countries that are less than entirely awesome? Some would argue that would include Russia and China, others would say the USA should be on a black list, too... What about Brazil under its current president? The UK? You can't stop anyone from using an open source product anyway, of course... It gets political quick, we've decided to stick to EU export regulations but it's a tough set of questions. Mother Teresa took money from dictators. Should she have? No?

It might seem easy to say, in a very principled way, no to all the above questions, but then your project won't be successful. And your project wants to make the world better, does it not?

Conclusion?

We discuss these things internally and try to be both principled and pragmatic. That is difficult and I would absolutely appreciate thoughts, feedback, maybe links to how other organizations make these choices. Please, post them here, or in the comments section of the original blog. I can totally imagine you'd rather not comment here as this blog is hosted by blogger.com - yes, a Google company. For pragmatic reasons... I haven't had time to set up something else!

There's lots of grey areas in this, it isn't always easy, and sometimes you do something that makes a few people upset. As the Dutch say - **Waar gehakt wordt vallen spaanders**.


PS and if you, despite all the hard questions, still would want to work at a company that tries to make the world better, we're hiring! Personally, I need somebody in marketing to help me organize events like the Nextcloud Conference, design flyers and slide decks for sales and so on... Want to work with me? Shoot me an email!

25 June, 2018

Working at Nextcloud

I've been around in communities like KDE, openSUSE, Mandrake/Mandriva and others... and various open source and closed companies. Seen some do a good job. Seen others be mismanaged. This one: the most fun. Serious.

Working at Nextcloud is special. For one, we're a distributed company. Is it hard? Well, yes and no. Working from home is great with such a motivated team with very little management overhead and good communication. Our company is entirely built on it, that is why it works.

As an example, while our head of sales lives in Hannover, the rest of the sales people is spread over Berlin, Switzerland, Stuttgart... Engineers can be found in Germany, Netherlands, Spain, even Croatia and as far as Cape Verde. I'm sure I forgot some countries. Our biggest office in Stuttgart has less people than we have in Berlin!

But we connect in person: roughly every second month, at a company-wide meeting in a single place, usually Stuttgart, for a full week of coding and having a great time. And once a year we go to Berlin for our conference, happening the last week of August! All those meetings are open, with often lots of community members participating in the whole process of designing and deciding around our software.

And yes, the sales people join there, too. I have NEVER worked in a company where the sales people, the marketing team and the engineers were so good with each other. Respect between these three departments is extremely rare, as I'm sure every one of my readers knows from experience.


Me handing the mic to the guys that started it all back in 2010


What else is crazy about Nextcloud? Here's another one: where lots of companies struggle to find good engineers, that is literally the LEAST of our problems. We drown in amazingly good CV's and have a big pool of enthusiastic, qualified engineers who contribute to Nextcloud and already know the code. I wish we could hire them all but growing more than 50-80% per year isn't really health for a company culture...

Also special: other companies struggle to get sales leads and pay lots of (advertising) money for them. We, we drown in leads... Even without marketing automation. Our biggest challenge, instead, is answering all the requests from companies that want to buy our product - we need more sales people!

Yes, we're a pretty unique company in how we approach open source business and we're successfully taking on much bigger companies. Yes, it works! Just check how we're doing on Google Trends. Love that!

If you want to work for us, especially in sales, or know somebody who should, tell me ;-)

Or first learn about us by meeting us - you're welcome at our conference! Or at one of our meetups, there's a monthly one in Berlin for example.


12 January, 2018

Nasty fall-out from Spectre and Meltdown

I guess it's hard to miss Spectre and Meltdown so you probably read about it. And there's more bad news than what's been widely reported, it seems.

You trust the cloud? HAHAHAHA

What surprised me a little was how few journalists paid attention to the fact that Meltdown in particular breaks the isolation between containers and Virtual Machines - making it quite dangerous to run your code in places like Amazon S3. Meltdown means: anything you have ran on Amazon S3 or competing clouds from Google and Microsoft has been exposed to other code running on the same systems.

And storage isn't per-se safe, as the systems handling the storage just might also be used for running apps from other customers - who then thus could have gotten at that data. I wrote a bit more about this in an opinion post for Nextcloud.

We don't know if any breaches happened, of course. We also don't know that they didn't.

That's one of my main issues with the big public cloud providers: we KNOW they hide breaches from us. All the time. For YEARS. Yahoo did particularly nasty, but was it really such an outlier? Uber hid data stolen from 57 million users for a year, which came out just November last year.

Particularly annoying if you're legally obliged to report security breaches to the users it has affected, or to your government. Which is, by the way, the case in more and more countries. You effectively can't do that if you put any data in a public cloud...

Considering the sales of the maximum allowed amount of stock just last November by the Intel CEO, forgive me if I have little trust in the ethical standards at that company, or any other for that matter. (oh, and if you thought the selling of the stock by the Intel CEO is just typical stuff, nah, it was noticed as interesting BEFORE Meltdown & Spectre became public)

So no, there's no reason to trust these guys (and girls) on their blue, brown, green or black eyes. None whatsoever.

Vendors screwed up a fair bit. More to come?

But there's more. GregKH, the inofficial number two in Linux kernel development, blogged about what-to-do wrt Meltdown/Spectre and he shared an interesting nugget of information:
We had no real information on exactly what the Spectre problem was at all
Wait. What? So the guys who had to fix the infrastructure for EVERY public and private cloud and home computer and everything else out there had... no... idea?

Yeap. Golem.de notes (in German) that the coordination around Meltdown didn't take place over the usual closed kernel security mailing list, but instead distributions created their own patches. The cleanup of the resulting mess is ongoing and might take a few more weeks. Oh, and some issues regarding Meltdown & Spectre might not be fix-able at all.

But I'm mostly curious to find out what went wrong in the communication that resulted in the folks who were supposed to write the code to protect us didn't know what the problem was. Because that just seems a little crazy to me. just a little.

28 September, 2017

Client-side, server-side and zero-knowledge end-to-end encryption in Nextcloud

End-to-end encryption in Android in action
Android encryption in action
Yesterday, Nextcloud published plans, designs and code for end-to-end encryption in the clients. A recent report from Forrester named data encryption as one of the top global Cybersecurity trends for 2017, so this is a big deal! I thought it'd be good to go over the differences between client-side, server-side and end-to-end encryption and position what we developed.

End-to-End Encryption

End-to-end encryption is usually associated with communication channels, think chat or video calls. Signal, Telegram and lately WhatsApp employ end-to-end encryption. So what does it mean?

The main property of end-to-end encryption is that the data is encrypted on the one end and decrypted on the other end, so only the sender and receiver can read it.

As an example, take the Nextcloud Video Calls app. When you share a link for a call and the other person joins, the Nextcloud Server essentially gives the other user the address of your computer and helps you connect to each other. It will also send signals when others join the call, when you mute and so on. But the actual call takes place between your system and that of your conversational partner, directly. And before it is sent out, your browser will encrypt the data for the other side to decrypt. This way, nobody in between, like your internet provider, can listen in!

The main downside of the term is that the definition of that 'end' can vary: you can say that normal https encryption is 'end-to-end', defining one end as the browser and the other end as the server. So this brings us to the difference between server-side and client-side encryption.

Server-side encryption

Server-side encryption serves to protect data on or going through a server: as soon as the data arrives, the server encrypts it. When you use a cloud storage like Amazon S3 or a Dropbox account or a FTP at another office with Nextcloud, our Server-side Encryption encrypts the data before it gets sent to the other storage and decrypt it only after it has been retrieved. Server-side encryption thus protects your data from access by a third party storage solution.

Note that encryption in the browser is essentially server-side encryption: the code that does the work comes from the server and thus the server controls what is going on. If a server is compromised, the attacker (or evil system administrator or government agency) can simply make a minor modification to that code so it gives them access to your private key!

When the data is on the server itself, however, the server admin has access to it as the keys are managed by the server. In case of Nextcloud, we encrypt that key with your login, making it impossible for the server to decrypt the files unless you are logged. That is called "protection of data at rest", but, of course, you log in all the time if you have the client running.

So the limitation of server-side encryption lies in what it does not protect you from: the server being compromised.

Client-side encryption

This is why server-side encryption is often contrasted with client-side encryption, which is what is employed by the end-to-end encryption Nextcloud introduced today. Where server-side encryption happens after transmission to the server, we encrypt the data on the Android, iOS or desktop client already. Then, only at the receiving end, it is decrypted again. That receiving end can be another device owned by the same user or a device owned by another user who has been given access to the data. But not anyone in between or otherwise not authorized! This is sometimes also called a zero-knowledge privacy: at no point in time can the server have any knowledge of the data.

The process of creating keys

A little bit about keys

Usually, public and private keys are used for the encryption and decryption. How does that work?

Everybody has a set of closely related keys, a 'public' and a 'private' key. They work a bit like a mail box works: anyone can throw a letter in the box, but only the mailman (or woman) can open and empty it. The public key is, as the name implies, public. Anyone can use it to encrypt something. But to decrypt the result, the private key is needed!

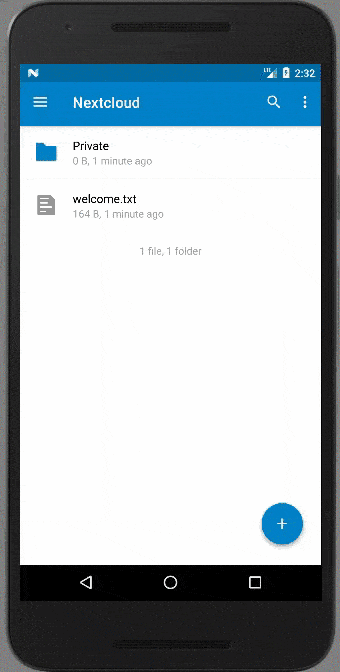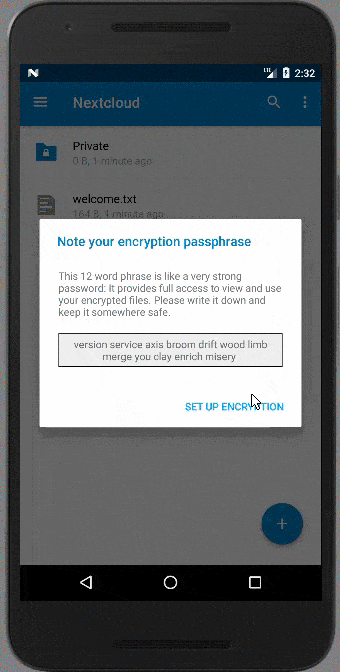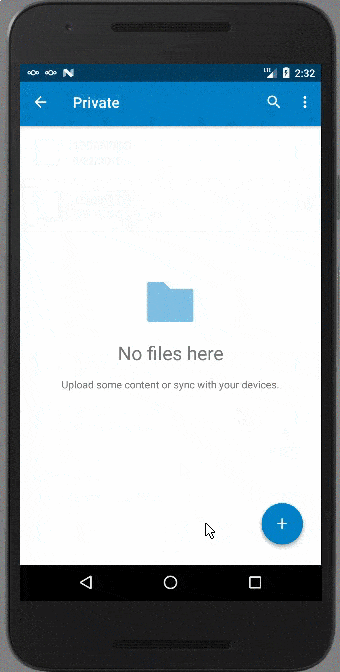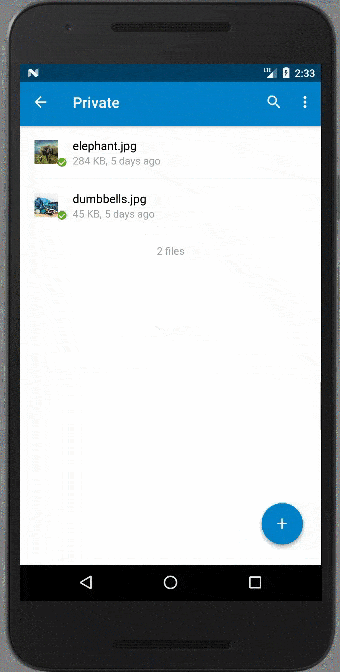
Nextcloud generates a public and private key pair the first time a user enables end-to-end encryption in their client. The public key gets signed by the server with 'certificate' to verify the user identity (our Cryptographic Identity Protection feature) and stored there for other users to encrypt files to that they wish to share. The private key gets encrypted with a locally, app-generated very secure and very long (12 word!) passcode which is displayed to the user and then the key gets stored on the server as well.

Another device owned by the user can download the private key, the user can enter the 12 word passcode to decrypt it, and this device will then also be able to encrypt and decrypt files. That is how you add your phone and desktop after you enabled end-to-end encryption on your laptop.

You can learn much more about exactly how the encryption and decryption work on the end-to-end encryption web page we made as well as the whitepaper you can download there.

Enterprise challenges

While consumers use end-to-end encryption for chat for years, larger organizations like companies and governments have struggled to find solutions that protect their sensitive data without disrupting productivity and legal requirements for audit logs.

Indeed, many solutions create a new layer over existing solutions like Box and Dropbox or have poor key management, making sharing cumbersome and less secure. A real enterprise solution needs to take the burden of complexity away from users and, if it needs to be anywhere, put it on the shoulders of the system administrators. Nextcloud has done exactly that, not even allowing users to create their own, potentially insecure password and making adding devices easy. The 12-word passcode can be recovered from any of the devices an user owns and it is possible to enable a system wide recovery key. If enabled, users will get warned of this and the system administrator gets to see and note down the key once and only once. After that, the code is destroyed and no attacker would be able to steal it, provided the server administrator puts it in a safe location: we'd recommend an actual safe.

Another important feature for enterprises is support for a Hardware Security Module which could be used to generate user certificates. Without it, our design does not allow users to switch identities (as this could be abused by an attacker with control over the server) but this restriction can be relaxed if a secure HSM is in the mix.

You can learn more on our webpage about end-to-end encryption!

01 August, 2017

Privacy, self-hosting, surveillance, security and open source in Berlin


August 22-29 we're organizing a conference to discuss and work on privacy, self-hosting, security and open source in Berlin: the Nextcloud Conference. We expect some 150-200 people to participate during a week of discussing and coding and, especially on the weekend, presenting and workshopping. So I thought I should blog about why should you be there and what can you expect?

If you care about protecting people from the all-pervasive surveillance, re-gain privacy and security of data and believe in self hosting and open source as solution for these issues, this is the place to be. Our event is special for two reasons:
The team that started ownCloud

We're doing it. And most of us have been, for a decade or more, in KDE, GNOME, SUSE, Ubuntu, phpBB and other earlier projects. The code we wrote has influenced millions of users already and we will go further and wider! Expect to meet people with a can-do attitude.

Second, Nextcloud has got a huge momentum, name recognition and has become one of the largest ecosystems in the open source privacy/self hosting area. It isn't just about us! Large companies, small startups and innovative individuals and small communities all over are building on and around Nextcloud. A few examples:

We are doers


So the Nextcloud conference is where you can find a wide range of individuals with interest, skills and ideas in the area of privacy and freedom activism, and they are doers! There is a reason we say "bring your laptop" on our conference page, though with that we don't mean we only want coders there!

Designers, activists and advocates are just as welcome. That is because Nextcloud is about more than technology. Frank is somebody who sometimes asks the hard questions and obviously it his vision is a strong diver, but we're all long time open source and/or privacy activists and deeply and personally motivated. Our entire community is built on drive, passion and a will to take on the challenges our society offers in the area of privacy, self determination, freedom.

That is the why you should be there. To help make a difference.

Now the what.

Getting Stuff Done

Our goal is to get work done; and facilitate communication and collaboration in our community. During the week, we simply provide space to talk and code (with wired and wireless network, Club Mate & other drinks, and free lunch). In the weekend, we have a program with talks & workshops. The setup is simple:

In the morning, everybody is in one room. First, we all hear from long time privacy activist and former Mozilla president Tristan Nitot. After that, community members working on a wide variety of interesting things around privacy/self hosting/open source and of course Nextcloud talk, shortly, about what they do. Just 3-8 minutes to give the audience an idea of their project, their plan, their idea, how to get involved, a call for action. Now again, everybody is in the room, so in the break, everybody has heard the same talks and has the same things to discuss! If you have something to add, be it about TOR, protests, encryption or anything else that is related: SUBMIT A TALK!

Collaboration & sharing ideas

Last year we announced the Nextcloud Box.
This year - be there and find out!
People can look up the speakers, join the meetings proposed and so on, in the afternoon. Because after lunch we have 2 (or more, not sure yet) tracks of workshops as well as hacking, coding and meetings in the coding rooms. Unconference style, so to say.

We now have several dozen talks and workshops already submitted and well over 100 people have registered but we are looking for more input in all areas so consider to be a part of this event!

It is free and open, supported by the TU Berlin which offers us a free location; and Nextcloud GmbH which sponsors drinks & practical stuff; and SUSE Linux which sponsors the Saturday evening party!

Learn more and register!

17 January, 2017

Happy Birthday ownCloud

Seven years ago at Camp KDE in San Diego, Frank announced a project to help people protect their privacy, building an alternative to Dropbox: ownCloud.

I was there, sharing a room with Frank at the infamous Banana Bungalow. Epic times, I can tell you that - there was lots of rum, lots of rain and loads of good conversations and making new friends.


Since then, a lot has changed. But the people who started building a self-hosted, privacy protecting alternative in 2010 and 2011 are still on it! In 2011, a first meetup was held, and the 5 participants at that meetup recently got on stage at the Nextcloud conference to recall some good memories:


Of course, today we continue the work at Nextcloud, that just yesterday published its latest bugfix- and security update. It is great to see so many people have stuck with us for all these years - just this month, the KDE sysadmins migrated their ownCloud instance to Nextcloud!

We'll keep up the good work and you're welcome to join, either if you're looking for a job or just want to code. In both cases I can promise you: working with such a motivated, dedicated, professional team is just plain amazing.

I also published a blog on our Nextcloud blog about this milestone.

EDIT: By the way - there's a meetup tonight in C-Base, B'lin, 19:00 - would be fun to drink a beer on ownCloud's birthday and talk about the future! Join! It will be at least until 10 or so, so if you can't be there before then - still come! ;-)

12 December, 2016

Wednesday: Release Party in Berlin!

On wednesday is our Nextcloud meetup and - Nextcloud 11 will be released, so let's make it a release party! Bring some snacks if you like, let's drink a beer or two, get our servers upgraded perhaps.
See and RSVP here:
When: Wednesday, December 14, 2016 7:00 PM
Where: C-Base, Rungestraße 20, 10179 Berlin
We're in the main room. C-Base is at the river, all the way to the end from the street. You're there if you get geeky tingles from the murals :D
I look forward to seeing you there, everyone's invited! That includes KDE friends, by the way, would be fun to see the bunch of you! You can RSVP in the comments here or on meetup.com...

CU there!

25 November, 2016

3 alternative reasons why you should test Nextcloud 11 Beta

On the Nextcloud blog I just published about the beta for Nextcloud 11. The release will deliver many improvements and is worth checking out in itself, plus I put a nice clickbait-style title and gave three reasons to test it.

But I actually have some more reasons to test. You see, Nextcloud is one of the tools we need to keep our democracy working. As Frank notes on his home page:
"Privacy is the foundation of democracy"
And he is completely right. So, here are three different reasons why you should test (and help improve) Nextcloud:

1. The USA is making a massive swing towards even more spying

Obama has done nothing to curb the growth of the NSA and the scope of its operations. Secret laws spiked under his watch. Many of the folks about to be put in power by President-elect Trump favor more spying, including on US citizens, expansion of the NSA, a crackdown on whistleblowers and more. Trump's pick for CIA director calls for Snowden's execution. For what I can only guess must be giving proof of illegal government spying to dangerous terrorists like the Washington Post and the Guardian, who proceeded to win a Pulitzer prize by disclosing this information irresponsibly to the US public.

In general, as somebody who changes his stance on hugely important and complicated issues like torture in under an hour, it is impossible to predict what Trump will do with the most powerful spying agency in the world under his control, but his appreciation for dictatorial figures like Kim Jong Il and Putin gives plenty cause for concern.

2. Britain isn't doing much better

I wrote about the Snoopers' charter just some days ago - this piece of legislation goes further than any earlier piece of spying law. It allows not only passive spying but also actively hacking devices from citizens.

3. Nor is Europe

The UK is not alone. Since Snowden, Europe has complained a bit about the NSA but seems to simply follow suit, rather than doing anything about it. Germany is even introducing a bill that will allow spying on foreign journalists.

Help out!

So, how can you help? Well, test Nextcloud 11 Beta, obviously. Help others to use it, get them involved. But it goes beyond Nextcloud - promote the use of and help improve tools like Tor, Signal and others, or democracy is screwed.

Edit: updated the blog 

22 November, 2016

Brittain’s Snoopers charter threatens your privacy

pic from the ZDNet article
The United Kingdom this week passed the so called Snoopers Charter, a law which forces UK internet providers to store the browsing history of UK citizens for a full year. You, your family, visitors or any devices in your household which have been hacked (the government is now allowed to do that, by the way) better not visit anything bad as the government can get their hands on this data quite easily. What does this mean and what can you do?

An attack on privacy

There is a global siege on privacy. Governments all over the world have introduced legislation (sometimes secret) which forces email, internet or data storage providers to track what you do and make that data available to their governments. This, of course, also means third parties who gain access to the storage systems can see and abuse it. And because so many of us have put so much of our data at just a few providers, we're at great risk as events like last week's shutdown of hundreds of Google accounts did show.

While Google, Dropbox and others lure customers in with 'free' data storage and great online services, governments benefit from centralized data storages as it makes it easy for them to hack in or demand data from these companies.

Why this surveillance?

While governments usually claim they need access to this data to find terrorists or child pornography, experts point out that it will not be helpful at all. As multiple experts (even internally) put it, growing the haystack makes it harder to find the needle. Intelligence agencies are swamped with data and nearly every terrorist attack in western states over the last decade took place despite the agencies having all information they would have needed to prevent it. The Paris attackers, for example, coordinated their attack using plain SMS messages. The Guardian thus rightly points out that:
"Paris is being used to justify agendas that had nothing to do with the attack"
which has become a familiar refrain after nearly every terrorist attack.

Indeed, we all know the argument But you have nothing to hide, do you? and indeed, we probably don't. But some people do, so they'll try to avoid being seen. That being illegal won't change their behavior...

And as Phill Zimmermann, the inventor of the PGP encryption pointed out:
"When privacy is outlawed, only outlaws will have privacy"

So not terrorists. Then what?

Experts agree that the vast majority of these surveillance and anti-privacy laws have little or no effect on real criminals. The crime syndicates, corrupt politicians and large corporations evading taxes and anti-trust/health/environmental laws, they DO have something to hide, and thus they would use encryption or avoid surveilled communication methods even if it were outlawed.

However, ordinary citizens, including grass-roots local activists, charitable organizations, journalists and others, who DO have nothing to hide, would be surveilled closely. And with that information, the real criminals mentioned earlier - crime syndicates, corporations or corrupt politicians - would have weapons in hand to keep these citizens from bothering them. Whistle blowers can be found out and killed (like in Mexico), journalists can be harassed and charged for trivial transgressions (like was recently done at the US pipeline protest) and charities can be extorted.

What can we do?

Luckily, there are initiatives like the Stanford Law Schools' Crypto Policy Project which aim to train, for example, journalists in the use of encryption. Tools and initiatives like Signal, PGP email encryption, Let's Encrypt and Nextcloud provide the ability for users to protect themselves and their loved ones from surveillance. More importantly, these at the same time making it harder and more costly to conduct mass surveillance.

There is nothing wrong with governments targeting criminals with surveillance but just vacuuming up all data of all citizens that might, some day, be used is a massive risk for our democracy. We all have a responsibility to decentralize and use tools to protect our privacy so those who need it (press, activists and others) have a place to hide.

29 September, 2016

Get started with Nextcloud App development in 6 easy steps!

The brand new app scaffolding tool in our app store
Last night, Bernhard Posselt finished the app scaffold tool in the app store, making it easy to get up and running with app development. I was asked on twitter to blog about setting up a development environment, so... here goes.

What's simpler than downloading a zip file, extracting it and running a command in the resulting folder to get an Nextcloud server up on localhost for hacking?

Yes, it can be that simple, though it might require a few minor tweaks and you have to make sure to have all Nextcloud dependencies installed.

Note that this is useful if you want to develop an Nextcloud app. If you want to develop on the Nextcloud core, a git checkout is the way to go and you'll need some extra steps to get the dependencies in place, get started here. Feedback on this process is highly appreciated, especially if it comes with a pull request for our documentation of course ;-)

Step 1 and Two: Dependencies

  • Install PHP and the modules mentioned here
    Your distro should make the installation easy. Try these:
    • openSUSE: zypper in php5 php5-ctype php5-curl php5-dom php5-fileinfo php5-gd php5-iconv php5-json php5-ldap php5-mbstring php5-openssl php5-pdo php5-pear php5-posix php5-sqlite php5-tokenizer php5-xmlreader php5-xmlwriter php5-zip php5-zlib
    • Debian: apt-get install php5 php5-json php5-gd php5-sqlite curl libcurl3 libcurl3-dev php5-curl php5-common php-xml-parser php5-ldap bzip2
  • Make Nextcloud session management work under your own user account.
    Either change the path of php session files or chmod 777 the folder they are in, usually something like /var/lib/php (debian/SUSE) or /var/lib/php/session (Red Hat).

The Final Four Steps


Nextcloud should present you with its installation steps! Give your username and password and you're up and running with SQLite.

Start with the app

Now you create a subfolder in the nextcloud/apps with the name of your app and put in a skeleton. You can generate an app skeleton really easy: use the scaffolding tool, part of our new app store for Nextcloud 11!

It's probably wise to now get going with the app development tutorial here. This isn't updated for the scaffolding tool yet, so you'll have a head start here. Be sure to check out the changelog, we try to make sure the latest changes are noted there so even if we didn't manage to fully update the tutorial, you can find out what will and won't work in the changelog. Also, be sure to update the links to get the latest dev doc - this all links to 11, once that is out it is probably better to directly target 12 and so on.

Help and feedback

Your input is very much welcome! If you run through these steps and get stuck somewhere, let me know and I'll update the documentation. Or, of course better still, do a pull request on the documentation right in github. You don't even have to do a full checkout, smaller fixes can easily be done in the web interface on github.

Last but not least, ask questions on our forums in the app dev channel or on IRC. Here is the Nextloud development IRC chat channel on freenode.net, also accessible via webchat.

Thanks, good luck, and have fun building Nextcloud apps!

05 September, 2016

Akonadi/KMail issues on Tumbleweed?

So if you, like me, have experienced how smoothly Akonadi deals with crashes and think it is still annoying, there's a solution. The problem is caused by Xapian which creates some nice backtraces but until it is fixed you are stuck with a crash every ~minute.

The solution is in this email from Christian Boltz:

I created a repo with the previous version of libxapian, and akonadi-* and baloo linkpac'd from Factory (so rebuilt against the old libxapian): https://build.opensuse.org/project/show/home:cboltz:branches:openSUSE:Factory

Packages at http://download.opensuse.org/repositories/home:/cboltz:/branches:/openSUSE:/Factory/standard/

Since I installed these packages (using zypper dup --from), I didn't see any akonadi crashes.

If someone wants to use the fixed packages _now_: I'll keep the repo as long as it's useful for me ;-) -> this is clearly caused by the libxapian update (libxapian22 -> libxapian30)


In other words, you fix it this way:

zypper ar http://download.opensuse.org/repositories/home:/cboltz:/branches:/openSUSE:/Factory/standard akonadi-fix
zypper ref
zypper lr
Now find the number of the new repository (akonadi-fix) and:
zypper dup --from 4
(where 4 is the number of the repo in my case).

Then OK the result and done, the mail client which, despite all its issues, continues to be the only one I can stand working with is smooth sailing again ;-)

Oh, to fix the mess Xapian made of the database, you probably should stop akonadi and remove the search DB, it will get re-indexed:
akonadictl stop
rm -rf ~/.local/share/akonadi/search_db
rm ~/.config/.baloorc
akonadictl start


Greetings from #Akademy2016 by the way!

02 September, 2016

Kickstarting conversations with lightning talks.

A lot of people are coming to the Nextcloud conference to discuss ideas they have with others and I've been telling them to submit a lightning talk. As that is the idea of the lightning track on Saturday and Sunday: present yourself and the project you (want to) work on, inspire, share ideas. That way, others can then find you and talk to you afterward!

Last year I wrote a longer article about that on opensource.com, but this is the gist of it: it is a conversation kickstarter! Our event is very hands-on (bring your laptop, we say!) and the program is mostly there to facilitate the natural flow of ideas and code.

So we have three kinds of sessions:

  • Keynote = inspiration. Everyone joints to listen to a fascinating story! Our keynote speakers are Karen and Jane.
  • Lightning talks = sharing. Everyone in one room listens to what others are thinking about, working on or inspired by. Then, after, you look each other up and start talking and doing! Think 'unconference'.
  • Workshops = learning and collaborating. They're coding, interactive, either teaching/learning or more "let's work on X for an hour together".

The event starts in two weeks at the TU Berlin: September 16-23 so it is time to book your trip. If you care about open source, privacy-protecting cloud services it is a great place to find like-minded folks!


What's coming?


Besides the keynotes by Karen Sandler (Managing DIrector at SFC) and Jane Silber (CEO of Canonical) We have some 30 sessions already submitted, just a selection:


More still coming, I know Cornelius Schumacher wanted to talk about the importance of privacy-protecting cloud services (if his family can miss him for the weekend...) and I still have some other talks to approve in the queue.
The gist of it is that we'll have a lot of technical people, the folks who wrote Nextcloud as well as many others who contributed and have been using it, from home users to enterprise and educational or government agencies - all together to discuss and work on where our technology is going.

Oh, and we have a surprise on Friday afternoon. ;-)

Check it out and see you there!

25 August, 2016

Latest attacks on privacy...

With the EU (in this case France and Germany) gearing up for another attack on privacy I'm quite happy and proud to have been part of the release of Nextcloud 10!

Privacy

It is the usual story: we should disallow companies from using perfect end to end encryption and force them to insert backdoors against terrorists.

Not that it would help - that's been discussed extensively already but in short:
  • If you have nothing to hide, you'll use a backdoored app and you're vulnerable to foreign (and your own) governments, terrorists (!), criminals and others who can abuse your data in more ways than you can imagine.
  • If you have something to hide, you can use 1000 different tools to do so and there is nothing government can do about that so you won't use a backdoored app.
  • And note that government has failed to even use fully unencrypted information to stop terrorist attacks so perhaps we should first see if they can actually get their act together there.
Now yes, backdooring all commonly used encryption apps will help a BIT, essentially only with the low level, common crime. So you might catch the dude who broke into your house and bragged about it to his friends over Whatsapp. You won't catch the terrorists plotting with Al Qaida (or whatever the terrorist organization du-jour) to blow up a train because they can simply get one of the many solutions out there to protect themselves.

Nor will you catch corrupt politicians or big companies doing nasty stuff, though I am quite certain the laws will be written in such a way that you can use them to go after people who actually try to expose such politicians or companies.

And I'm also quite certain companies will use this as an excuse to not implement proper protection in their products so you can continue to stop pacemakers remotely or disable the brakes in cars over the internet.

Generally, laws targeting encryption and terrorism do more to harm whistleblowing than terrorism and are thus promoting corruption and bad, unsecure products.

These laws will literally cost lives. Not save any.

And it is exactly why Frank started ownCloud and why we continue to develop that vision at Nextcloud. And keep developing new features, like the File Access Control app which can provide an extra protective layer around your data. I for one certainly can use that app and exactly in the way described in that blog! So much for 'enterprise only features'.


Get it and migrate today. You and your data deserve it!